Exclusive insights into the latest Threat Intelligence. Keeping constant watch over the cyber and geopolitical landscapes so you don’t have to.
Monthly Threat Intelligence Report
Ransomware activity continued to rise throughout August 2026, reaching a new year-to-date high. August highlighted the evolving nature of cyber threats, from the emergence of new ransomware groups to the growing security challenges associated with advanced AI systems.
August 2026 key insights:
- 1,073 ransomware attacks were recorded globally in August, representing a 12% increase compared to July and the highest monthly total recorded in 2026 to date.
- Industrials remained the most targeted sector, accounting for nearly a third of all attacks with 329 incidents (31%), followed by Consumer Discretionary with 185 attacks (17%).
- North America remained the most targeted region, accounting for 473 attacks (44%), followed by Europe with 276 attacks (26%).
- Qilin overtook The Gentlemen as the most dominant threat group, responsible for 15% of all attacks.
- NCC Group's DFIR team examined Aurora, an emerging ransomware group using established techniques such as VPN exploitation, credential harvesting and data extortion to target organisations across multiple sectors.
- The OpenAI-Hugging Face incident highlighted the growing security and governance challenges associated with increasingly capable autonomous AI agents operating in real-world environments.
August's findings demonstrate that both established and emerging threats continue to evolve. Record ransomware activity and the rapid rise of groups such as Aurora show that proven attack techniques remain highly effective, while the OpenAI-Hugging Face incident illustrates the growing security implications of increasingly capable AI systems operating with greater autonomy. Together, these developments reinforce the need for organisations to strengthen foundational cyber security controls while ensuring that emerging technologies are deployed within robust security and governance frameworks.
Mini Shai-Hulud and Open-Source Supply Chain Attacks
NCC Group is monitoring the ongoing and rapidly evolving wave of Shai-Hulud supply chain attacks.
This report covers the most recent wave of Shai-Hulud activity (Mini Shai-Hulud, Miasma and Hades), observed throughout May and early June 2026. As well as supporting triage of active infections, it provides guidance for defenders building security postures that address the structural risks of open-source package reliance, rather than simply ingesting wave-specific IOCs in response to each new campaign.
Monthly webinar
Our team of Threat Intel experts keep a constant watch over the cyber and geopolitical landscape, so you don’t have to.
Introducing our monthly highlights webinar, giving you further insight and exclusive access to what's going on now. Join our Global Head of Threat Intelligence, Matt Hull, each month for:
- A deeper understanding of the latest report findings
- A look at emerging trends by region and sector
- Insight into new threat actors
- Spotlight on the most impactful active cyber threats
Our next webinar will take place on October 20th 2026, 4pm BST.
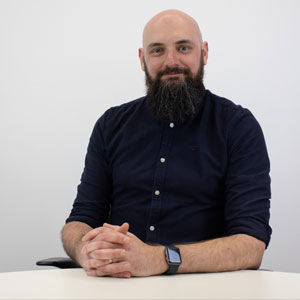
Matt Hull
VP, Cyber Intelligence and Response
Subscribe to our monthly reports and webinars for the latest on recent and emerging advances in the threat landscape and a deep understanding of the latest Tactics, Techniques and Procedures (TTPs) of threat actors.
Cyber Threat Intelligence report archive
On demand videos
Missed a webinar? Find every past recording in our showcase:
View now
Never miss any intelligence.
Hit the button below to get our monthly reports and highlight webinars straight to your inbox.